Endpoint security
& hardening.
Designing and validating Windows endpoint controls through Microsoft Intune, Defender and application-control policies.
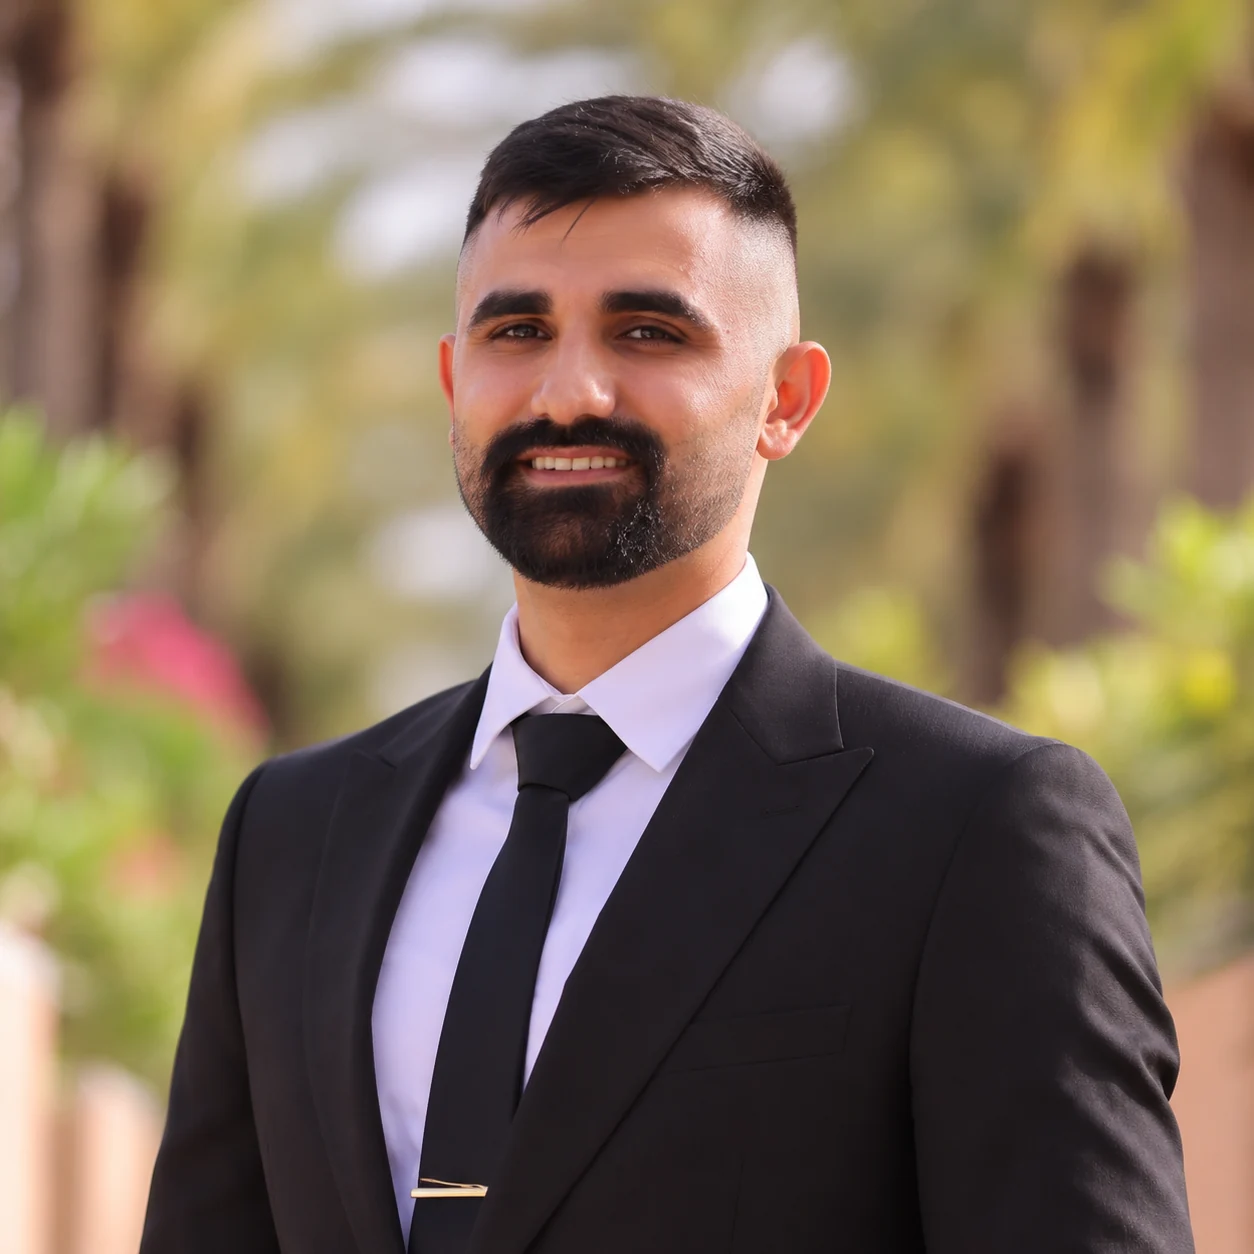
I'm Saleh Abou Hassan. I engineer practical security across enterprise endpoints, identity, cloud and infrastructure — then validate that the controls actually work.
Understand the risk. Engineer the control. Validate the outcome.
01 / SELECTED WORK
A selection of hands-on engineering, investigations, infrastructure design and controlled lab work. Technical detail without exposing private environments.
Designing and validating Windows endpoint controls through Microsoft Intune, Defender and application-control policies.
Analyzing endpoint telemetry, processes and file evidence to distinguish legitimate activity from threats.
Secure connectivity and access-control workflows using FreeRADIUS, VPN, Docker and Proxmox.
Hands-on authorized labs covering crash analysis, debugging, exploit fundamentals and defensive mitigations.
* Visuals are illustrative. Project descriptions are deliberately generalized; no private customer data, telemetry, confidential systems or unverified results are published.
02 / CORE EXPERTISE
Strong security comes from knowing how systems behave — and where assumptions fail.
Microsoft Defender for Endpoint, Intune, Entra ID, endpoint configuration and security policy validation.
Endpoint investigation, alert triage, security telemetry, event correlation and PowerShell-assisted analysis.
VPNs, identity-aware access, FreeRADIUS, virtualization, Microsoft 365 administration and cloud security practices.
Authorized penetration testing labs, vulnerability analysis, risk assessment methods and governance fundamentals.
03 / THE PERSON
My work lives where engineering decisions become security decisions.
I’m a Senior Security Engineer with hands-on work across Microsoft security tooling, infrastructure access, endpoint investigations and system hardening. I value clarity over noise: understand the environment, investigate the risk, build a control and test it properly.
Outside day-to-day defensive engineering, I explore responsible offensive testing in lab environments and the connection between technical controls, risk and governance.
04 / PROFESSIONAL DEVELOPMENT
Certifications belong here only when earned and verifiable. This section is ready for your actual credentials, issuer details, badges and verification URLs.
Verified certifications and training will be published here when the details are provided. No placeholder badges or invented certificates.
Interested in security engineering, practical defense and thoughtful technical challenges? Let’s connect.